The Workstation Blog
Security
Posts tagged Security.
Put Internal Apps Behind Your VPN, Without Rebuilding Them
Staging sites and admin panels are often 'private' because of an IP allowlist. Put them behind the wslvpn Zero Trust VPN, enforced at the WSLProxy edge: check the tunnel and the person, fail closed, and see why someone was blocked. One field per domain, no app changes, no reload.
 Balinder WaliaRead
Gateway API Shifts Cluster Networking: An Ownership Model for the Edge
Ingress is frozen and Ingress NGINX is retired. Gateway API replaces one shared object with resources owned by platform and application teams, joined by explicit handshakes. Here is what that means for platform design, RBAC, topology and CRD ownership.
Agentic AI in Production: Permissions, Approval Gates, Traces and Evals
A practical playbook for running AI agents in production: classify every tool by side effect, gate mutations behind a human, set hard stop conditions, trace each step with OpenTelemetry and evaluate continuously.
MCP for DevOps: Give Agents Pipeline Context Without the Keys
How platform teams can use the Model Context Protocol safely: start with read-only servers and scoped identities behind a gateway, trace every tool call, and add write tools only behind human approval. Includes RBAC, tool and task examples.
Gemini 4 Argon: What It Means for Your Team, and Where to Use It First
Gemini 4 Argon is built to work for hours on one measurable problem. Here is what shipped, the real costs, and how to pilot it safely on your own backlog.
Balinder WaliaRead 
WSL Vault for Compliance: One Tenant Never Opens Another’s Secrets
How WSL Vault keeps app, team, and environment tenants cryptographically isolated — so a stolen root-style token cannot empty the estate — and why dual-tenant control beats secrets sprawl.
Balinder WaliaRead 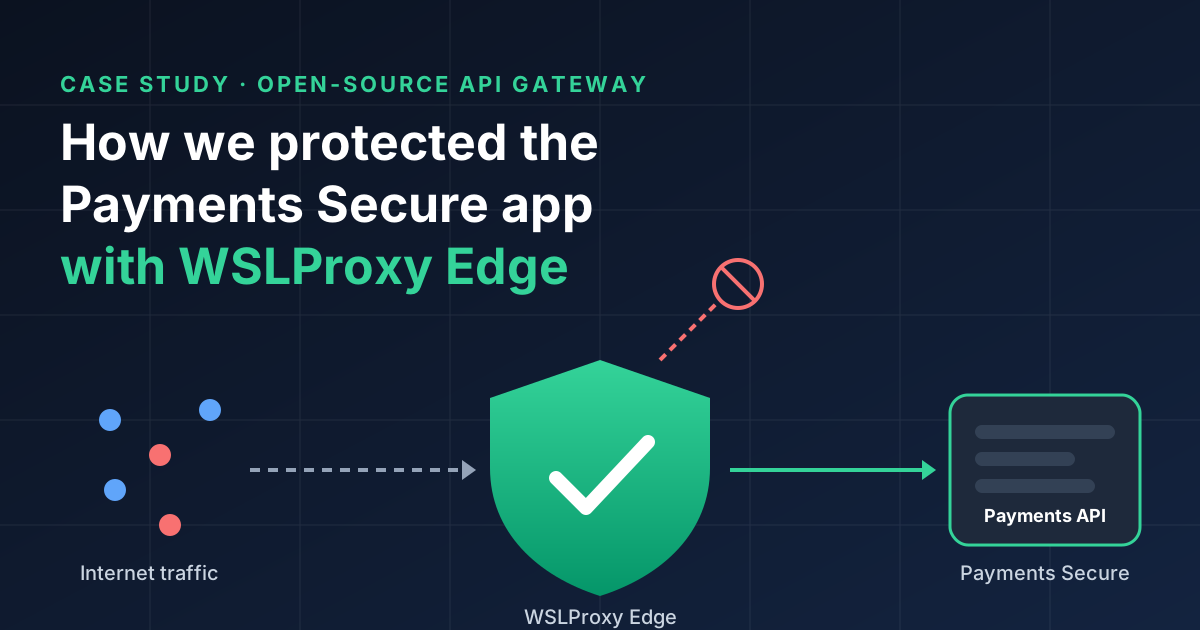
How We Protected the Payments Secure FinTech App with WSLProxy Edge, an Open-Source API Gateway
How we put WSLProxy Edge, our open-source API gateway, in front of Payments Secure (payments-secure.fictionally.org): real-IP checks, scanner detection, login throttling and audit logs, rolled out safely in audit mode.
Balinder WaliaRead 
WSLVault: Why AI Agents Need Cryptographic Secrets Isolation
AI agents use secrets at machine speed across tools and tenants. WSLVault seals per tenant so a shared platform never leaks another team's plaintext.
Balinder WaliaRead